
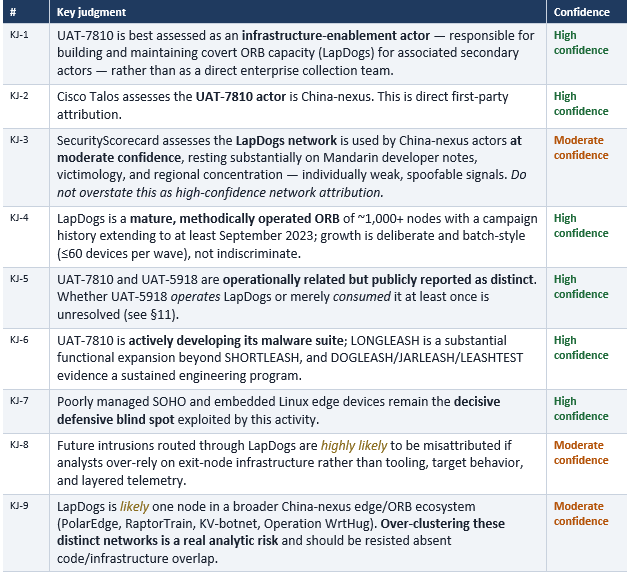
Key Judgments (BLUF)
UAT-7810 is best understood not as a front-line collection team but as a China-nexus infrastructure-enablement actor that builds and maintains the LapDogs Operational Relay Box (ORB) network for downstream operations. The judgments below carry disaggregated confidence tags: attribution of the actor (UAT-7810) and of the network (LapDogs) rest on different sources and different confidence levels, and are stated as such.
1. Scope & Analytic Approach
This product characterizes the modus operandi of UAT-7810 and the LapDogs ORB across its lifecycle: actor role, ORB mechanics, campaign timeline, the LEASH-family malware ecosystem, infrastructure and tradecraft, and defender implications. It closes with an ATT&CK mapping (Appendix A), an intelligence-gaps register (§11), consolidated IOCs (Appendix B), and a graded source register (References).
Two disciplines are applied throughout. First, observed versus inferred is kept explicit: network artifacts, malware capabilities, and vendor telemetry are stated as fact and cited to the reporting party, while operator identity, tasking model, and inter-actor relationships are labeled as assessment. Second, the ORB problem imposes a specific caution — an exit node is not an operator. A confirmed LapDogs node identifies infrastructure, not the intrusion actor using it; attribution of any downstream operation requires separate analysis of tooling and target behavior.
2. Actor Profile & ORB Ecosystem
2.1 UAT-7810 as an infrastructure operator
Cisco Talos describes UAT-7810 as an APT responsible for maintaining and proliferating the LapDogs ORB network and assesses with high confidence that it is China-nexus, most likely tasked with establishing ORB networks that associated secondary actors can leverage against high-value targets. That is unusually direct public language for an infrastructure-support role, and it reframes the analytic question from “who ran this intrusion?” to “who built the network layer that made multiple intrusions possible?” SecurityScorecard reached a closely aligned functional picture from network-wide node hunting, though it is more cautious on operator identity (§2.3).
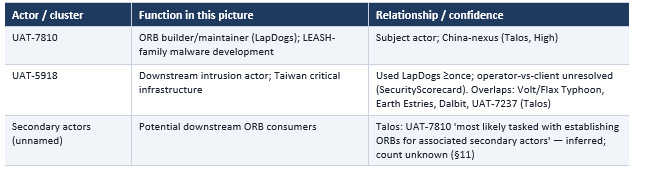
2.2 Actor relationship map
Public reporting supports a cautious functional map, not a hierarchy chart. Talos explicitly separates UAT-7810 (ORB builder) from UAT-5918 (downstream intrusion actor); SecurityScorecard found UAT-5918 used LapDogs at least once but could not confirm whether it operated the network or merely consumed it. Talos has separately linked UAT-5918 to overlaps with Volt Typhoon, Flax Typhoon, Earth Estries, and Dalbit activity, and to the related cluster UAT-7237 — situating this activity inside a dense China-nexus ecosystem rather than a single group.
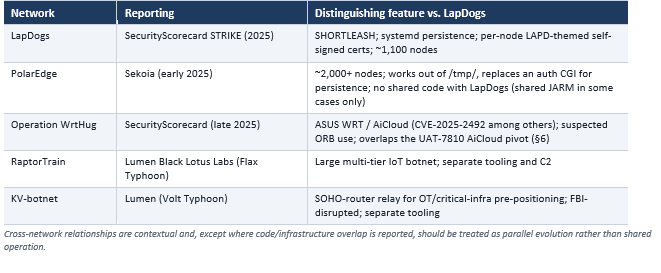
2.3 ORB-ecosystem crosswalk (resist over-clustering)
LapDogs belongs to a wave of China-nexus edge/ORB networks. Situating it aids the reader, but these are distinct operations that share only the edge-device tradecraft pattern; conflating them because they all touch routers and expose odd-port TLS is a documented analytic error. The crosswalk below is for context and de-confliction, not equivalence.
3. Why ORB Networks Change the Defensive Problem
Mandiant’s framework is the clearest explanation of why ORB networks matter. ORB networks combine leased VPS instances with compromised routers and IoT devices to provide relay, traversal, and exit capacity that conceals operator origin. Because the infrastructure has a short indicator lifespan and may be administered by entities separate from the APT operators who use it, ORB networks accelerate “IOC extinction” — static network indicators decay so fast that IOC-centric detection alone becomes unreliable. The strategic consequence for defenders: pivot from chasing individual C2 addresses to fingerprinting the infrastructure behavior (certificates, JARM, service anomalies) and hardening the edge devices that become nodes.
LapDogs fits this model with unusually concrete fingerprints. Nodes generate per-node self-signed certificates with LAPD-themed metadata, expose a shared JARM value, and cluster by issuance time, port assignment, geography, and ISP. In practice LapDogs is a reusable stealth layer for reconnaissance, actor browsing, staging, proxying, and potential downstream C2 — not a classic DDoS/spam botnet.
4. Campaign Timeline
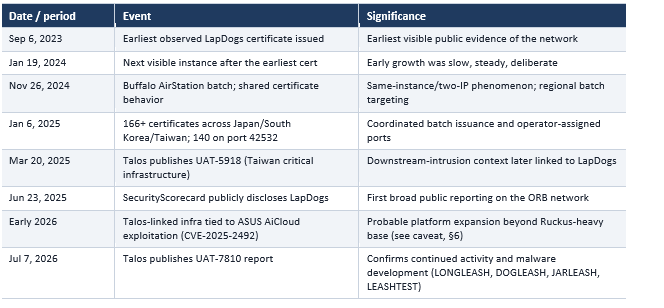
SecurityScorecard’s timeline evidence deserves weight because it ties certificate issuance to intrusion grouping: on January 6, 2025 it observed 166+ certificates generated within seconds of one another across three countries, 140 of them served on operator-assigned port 42532. That is the signature of a managed relay network, not opportunistic internet-scale infection.
5. The LEASH-Family Malware Ecosystem
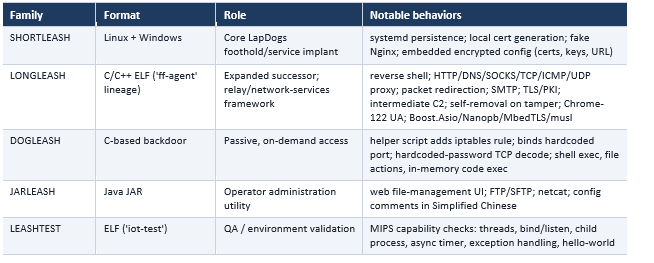
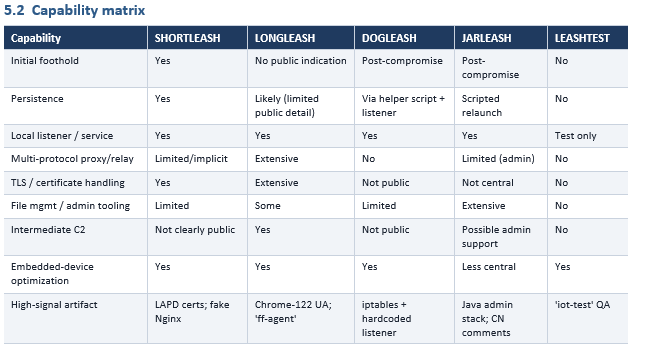
SecurityScorecard identified SHORTLEASH as the original LapDogs backdoor; Talos (July 2026) reported UAT-7810 developing a more capable successor, LONGLEASH, and added DOGLEASH, JARLEASH, and LEASHTEST. The progression from a stealthy foothold-and-relay implant toward a broader network-operations framework is the clearest evidence that UAT-7810 runs an infrastructure program, not a one-off campaign.
5.1 Analytic reading of the malware suite
• SHORTLEASH turns a neglected router or embedded Linux host into a reusable ORB node that still resembles a mundane appliance — stealth, persistence, and network utility in one implant.
• LONGLEASH is the decisive signal: a purposeful relay/network-services framework for embedded environments, including intermediate-C2 behavior (fetch from the original controller, forward to peers) — exactly what makes ORB infrastructure valuable to multiple follow-on actors.
• DOGLEASH favors low-noise, service-oriented persistence; deployment leaves huntable traces (shell-script execution, iptables changes, new TCP listeners on devices that should rarely change behavior).
• JARLEASH is an operator administration layer, not the core relay; Simplified-Chinese config comments add corroborative attribution weight but are, by themselves, a weak/spoofable signal (§KJ-3).
• LEASHTEST evidences an engineering/QA workflow for cross-platform (MIPS) maintenance — a stronger indicator of a sustained ORB program than any single implant.
6. Infrastructure & Tradecraft
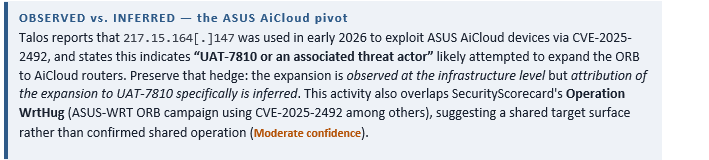
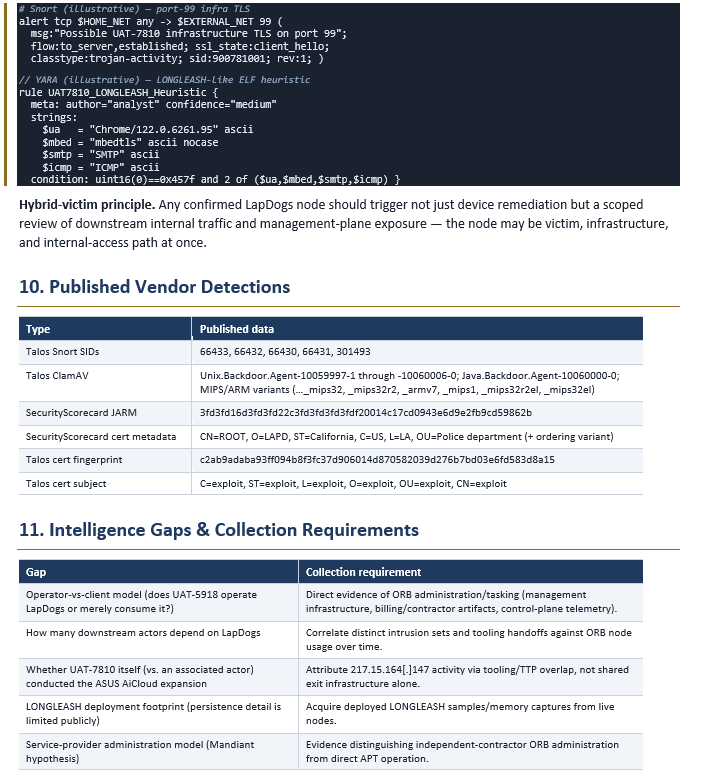
UAT-7810 payload servers. Talos identified at least four servers hosting MIPS/ARM/x64 payloads: 194.233.92[.]26, 217.15.160[.]247, 217.15.164[.]147, and 95.182.100[.]231. Two exposed a TLS service on port 99 with a certificate fingerprint c2ab9ada…583d8a15 whose subject fields were all set to exploit.
LapDogs network fingerprints. SecurityScorecard tied LapDogs to the northumbra[.]com domain family, a LAPD-themed self-signed certificate (initially observed with hardcoded C2 www.northumbra[.]com), and a stable JARM fingerprint 3fd3fd16…9862b, which surfaced 1,000+ active nodes globally. Certificates appear generated locally per node, with ports assigned by intrusion set — so issue-time, port, and country form a triangular relationship that let 162 intrusion sets be reconstructed.
De-confliction from PolarEdge. LapDogs and PolarEdge (Sekoia) share a JARM value in some cases and both target edge devices, but they are distinct: LapDogs persists via systemd service insertion and per-node cert generation, while PolarEdge works out of /tmp/ and, in one pattern, replaces an authentication CGI script for persistence, with no shared code reported. Defenders should avoid over-clustering the two on JARM alone.
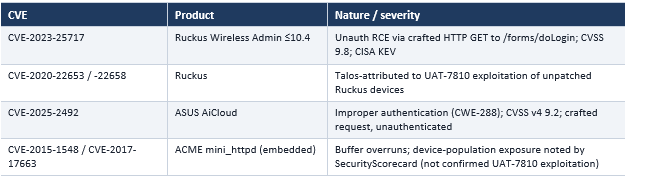
Device population exposure. Beyond the CVEs UAT-7810 is reported to exploit (§9), SecurityScorecard noted the LapDogs device population was broadly vulnerable to legacy embedded-web-server flaws — CVE-2015-1548 and CVE-2017-17663 (ACME mini_httpd buffer overruns) — alongside outdated GoAhead and DropBear SSH components. This distinguishes what the fleet was exposed to from what the actor is confirmed to have exploited.
7. Defender Implications by Audience
7.1 Executives
Internet-facing edge devices are strategic infrastructure, not convenience hardware. A compromised router can become a deniable relay, a staging layer, or a hybrid victim that grants access to the internal network it serves. The risk is magnified by ownership ambiguity: SOHO-class devices, remote-office kits, aging wireless gear, and OEM appliances frequently sit outside the security program. LapDogs exploited exactly that governance gap. A board-level response should fund device inventory completeness, owner accountability, firmware-lifecycle policy, passive TLS visibility, and external attack-surface reduction — and require breach-notification clauses from MSPs managing edge devices.
7.2 SOC teams
Infrastructure-centric hunting must complement malware detection. High-value anchors include the SecurityScorecard JARM fingerprint, LAPD-themed certificate subjects, Talos’ exploit certificate on port 99, suspicious router-originated egress, and odd high-port service exposure (e.g., 42532) during clustered campaigns. Hunt behavior, not just names: DOGLEASH implies iptables manipulation, new inbound listeners, and shell-script-driven deployment; SHORTLEASH implies new systemd service files, fake Nginx banners, and local certificate generation tied to compromise timing. Passive TLS, NetFlow, DNS telemetry, configuration-drift monitoring, and router/appliance syslog are disproportionately valuable here.
7.3 Infrastructure & vulnerability management
Reduce the exposed edge-device attack surface. Where devices are end-of-life or cannot be patched quickly, apply exposure reduction: disable WAN-facing administration, disable vulnerable remote-access features (e.g., AiCloud), restrict management networks, rotate credentials, and rebuild or replace suspected nodes rather than rebooting them. LapDogs was designed for persistence under normal uptime; “it came back after a reboot” is the wrong mental model. Any confirmed node is potentially victim, infrastructure, and internal-access path simultaneously — so remediation must include a scoped review of downstream internal traffic, privileged access, and management-plane exposure.
8. MITRE ATT&CK Mapping
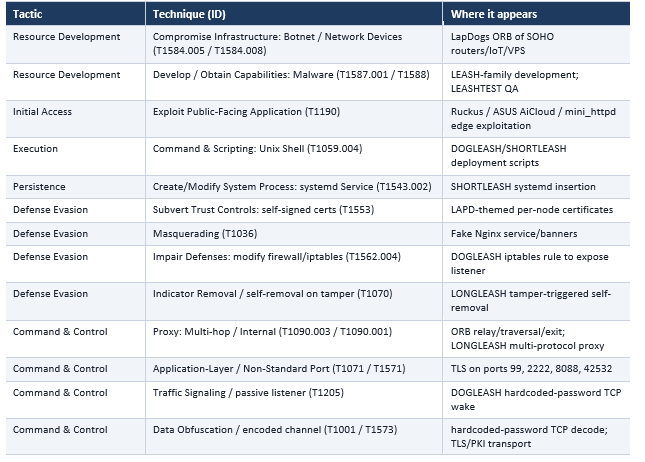
The report’s prose is technique-rich but was previously unmapped. The starter mapping below covers the ORB build/maintain lifecycle and the LEASH family; validate against recovered samples.
9. Detection & Hunting
Start at the network and move inward: pivot from a known-bad internet endpoint, to a suspicious TLS service on an edge device, to local forensic checks (systemd units, iptables changes, downloaded helper scripts). Talos published official Snort SIDs (66430–66433, 301493) and ClamAV signatures for the 2026 families — treat these as one layer, not the whole strategy.
9.1 Exploited vulnerabilities (for edge-fleet remediation)
9.2 Illustrative hunting aids (analyst-authored)
The examples below are analyst-authored hunting aids derived from publicly reported indicators. They are not vendor-issued signatures and should be validated in a lab before production; Talos’ official SIDs remain authoritative.
12. Outlook (12-Month)
• UAT-7810 will almost certainly continue developing the LEASH family and expanding node platforms (MIPS/ARM/x64; ASUS/Ruckus and beyond), given the QA discipline evidenced by LEASHTEST (High confidence).
• China-nexus reliance on ORB/edge relay infrastructure will very likely keep growing, eroding IOC-centric detection and shifting advantage to passive-TLS/JARM and edge-inventory programs (Moderate confidence).
• Downstream operations routed through LapDogs are highly likely to be misattributed where analysts anchor on exit-node infrastructure rather than tooling and target behavior (Moderate confidence).
• Over-clustering of distinct edge/ORB networks (LapDogs, PolarEdge, WrtHug, RaptorTrain, KV-botnet) is likely to recur in open reporting; maintain code/infrastructure-overlap standards before merging clusters (Moderate confidence).